How to Set Up a Pi-hole Network Ad Blocker (Step-by-Step)
Online advertisements, tracking telemetry, and malicious redirect domains consume bandwidth and compromise user privacy across modern home networks. While browser extensions can block intrusive scripts on desktop computers, they offer zero protection for smart TVs, streaming media sticks, mobile gaming apps, and smart home appliances. The most effective way to eliminate intrusive tracking across every connected device is to set up Pi-hole as a network-wide DNS sinkhole.
When you set up Pi-hole on your local network, it intercepts Domain Name System (DNS) queries generated by your devices. If a query matches an entry on an ad-serving or tracking blocklist, Pi-hole drops the request before the ad asset can ever download.
In this comprehensive tutorial, we walk you through everything needed to set up Pi-hole successfully using Docker on a mini PC or server, configure upstream recursive DNS, point your home router to your new sinkhole, and curate ad-blocking lists.
Recommended Hardware to Run Pi-Hole
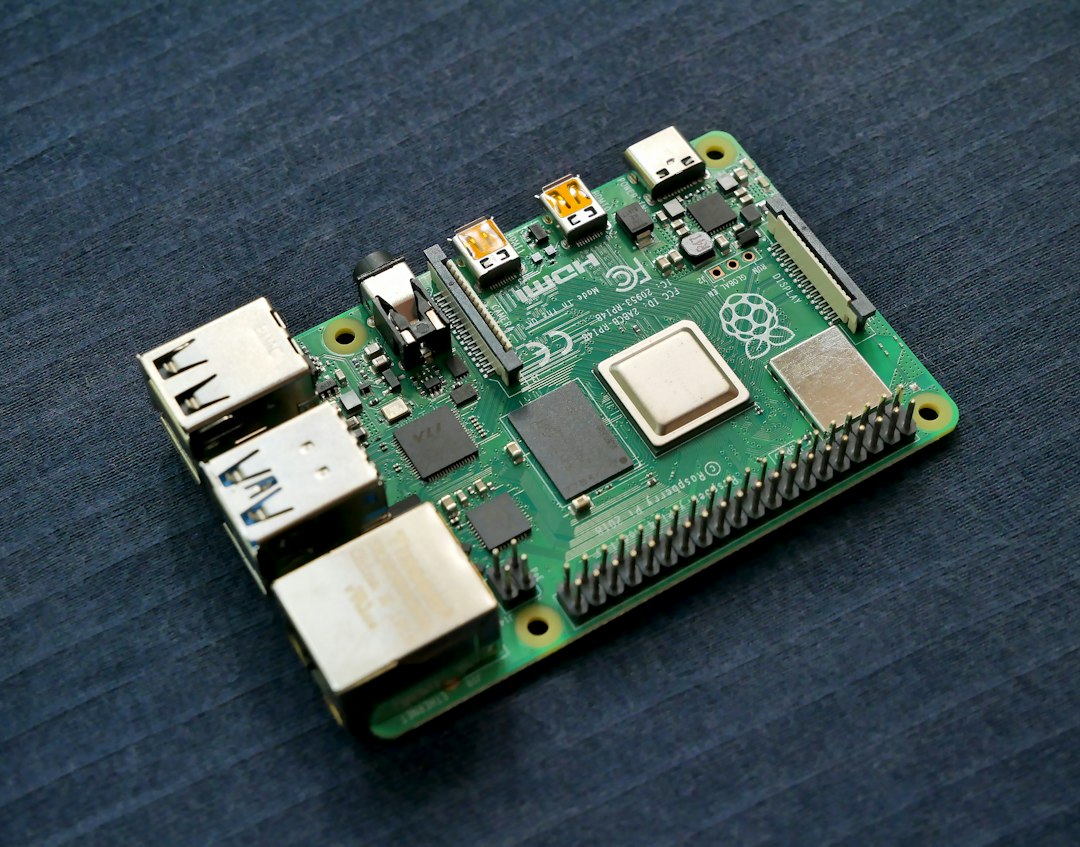
Pi-hole is exceptionally lightweight and consumes minimal memory and CPU cycles. It can run on low-power hardware that sips electricity continuously.
1. Intel N100 Fanless Mini PC (Beelink EQ12)
An Intel N100 or N95 mini PC is our top recommendation for running Pi-hole alongside containerized home services like Home Assistant, WireGuard, and media servers. It features low idle power consumption (under 8 watts) and dual 2.5GbE network interfaces.
💰 Buy on Amazon → Beelink Mini PC
With 16GB of DDR5 RAM and NVMe storage, a mini PC delivers snappy DNS lookup caching that handles thousands of queries per minute effortlessly. Running Linux containers on dedicated hardware gives your home network continuous uptime.
2. Dedicated Single-Board Computer / Appliance (Home Assistant Green)
If you prefer a plug-and-play appliance that operates silently in your networking cabinet, dedicated ARM-based hardware is ideal. Running Pi-hole inside Home Assistant OS or container environments provides an easy maintenance path.
💰 Buy on Amazon → Home Assistant Appliance
This compact form factor consumes negligible power while offering reliable 24/7 service availability.
3. Managed Smart Switch (TP-Link TL-SG116E)
Connecting your DNS server via physical Gigabit Ethernet rather than Wi-Fi is essential for low latency and zero packet loss. A reliable multi-port switch keeps your home infrastructure stable.
💰 Buy on Amazon → TP-Link Managed Switch
With hardware QoS and port monitoring, a managed gigabit switch ensures your DNS server always receives top scheduling priority.
How Pi-hole DNS Sinkholing Works
Every time a smart television, laptop, or smartphone connects to an online service, it performs a DNS lookup to translate human-readable domain names into routable IP addresses.
When you set up Pi-hole as your primary network DNS server:
– Query interception — Client devices forward all DNS requests directly to the local Pi-hole instance.
– Blocklist evaluation — Pi-hole compares the requested domain against hundreds of thousands of entries stored in its gravity database.
– Null routing — If the domain is identified as an ad server, telemetry tracker, or malware host, Pi-hole immediately responds with a null IP address (0.0.0.0) or NXDOMAIN code. The client device never initiates a network connection to the advertising host.
– Upstream forwarding — If the requested domain is legitimate, Pi-hole forwards the request to your configured upstream DNS provider (such as Quad9, Cloudflare, or local Unbound) and caches the result for future requests.
– Local DNS caching — By caching valid responses in memory, subsequent requests for frequently visited domains are resolved in less than one millisecond, noticeably speeding up general web browsing.
Step-by-Step Guide to Set Up Pi-Hole with Docker
Deploying Pi-hole inside a Docker container ensures rapid deployment, easy version upgrades, and isolated environment dependencies.
Step 1: Prepare the Host System and Install Docker
Ensure your host Linux system (such as Debian, Ubuntu, or Alpine Linux) is fully updated. Install Docker and the Docker Compose plugin using official system repositories:
sudo apt update && sudo apt upgrade -y
sudo apt install -y curl docker.io docker-compose-plugin
sudo systemctl enable --now docker
On systemd-based Linux distributions, the local systemd-resolved stub resolver often binds to port 53 by default. Disable the stub listener to free port 53 for Pi-hole:
sudo sed -r -i.orig 's/#?DNSStubListener=yes/DNSStubListener=no/g' /etc/systemd/resolved.conf
sudo systemctl restart systemd-resolved
Step 2: Create the Docker Compose Configuration
Create a dedicated directory for your Pi-hole deployment and generate a compose manifest:
mkdir -p ~/pihole && cd ~/pihole
nano docker-compose.yml
Paste the following Docker Compose configuration into the editor:
version: "3"

services:
  pihole:
    container_name: pihole
    image: pihole/pihole:latest
    restart: unless-stopped
    ports:
      - "53:53/tcp"
      - "53:53/udp"
      - "80:80/tcp"
    environment:
      TZ: 'America/New_York'
      WEBPASSWORD: 'YourSecureAdminPasswordHere'
      FTLCONF_LOCAL_IPV4: '192.168.1.50'
    volumes:
      - './etc-pihole:/etc/pihole'
      - './etc-dnsmasq.d:/etc/dnsmasq.d'
    cap_add:
      - NET_ADMIN
Make sure to replace 192.168.1.50 with your host server static local IP address, and choose a strong administrator password.
Step 3: Launch the Container and Access Admin Web Interface
Start the container in detached background mode:
docker compose up -d
Verify that the container is running and listening on ports 53 and 80:
docker ps
Once the container is initialized, open your browser and navigate to the web administration portal at your server IP on path /admin to log in and inspect the dashboard metrics.
Configuring Router DNS Settings
To protect every device automatically without manually editing network adapters on individual phones and computers, update your home router DHCP settings.
- Log in to your router admin panel — Access your gateway management interface (typically
192.168.1.1or192.168.0.1). - Locate DHCP / LAN DNS settings — Navigate to the LAN configuration page where DHCP server settings are defined.
- Set Primary DNS to Pi-hole IP — Enter your Pi-hole host IP address (e.g.,
192.168.1.50) in the Primary DNS field. - Leave Secondary DNS blank or set to secondary Pi-hole — Do NOT set a public DNS provider (like 8.8.8.8) as Secondary DNS. Client operating systems will query secondary servers in parallel, allowing ad traffic to bypass blocking.
- Renew DHCP leases — Save router settings and reconnect client devices to assign the new DNS parameters.
Advanced Privacy: Adding Unbound Recursive DNS
When you set up Pi-hole with third-party upstream DNS providers, those providers can still log your outbound domain lookup requests. Integrating Unbound creates a self-hosted recursive DNS resolver that queries root name servers directly.
Unbound contacts root authoritative nameservers directly over DNSSEC-validated connections, caching answers locally on your server. This eliminates middleman logging and strengthens DNS integrity against cache poisoning attacks.
Setting up Unbound inside Docker or directly on the host machine takes only a few minutes. You simply configure Unbound to listen on local port 5335, and then specify 127.0.0.1#5335 as Pi-hole custom upstream DNS server. This creates an end-to-end private resolution pipeline where no single corporate entity tracks your browsing habits.
For additional network hardening strategies, review our guides on cybersecurity best practices for home networks and how to set up a secure home firewall gateway. If you are provisioning dedicated hardware, consult our walkthrough on building a low-power home server and our pfSense vs OPNsense comparison.
Curating Blocklists and Whitelists
Pi-hole includes the StevenBlack unified hosts blocklist by default, which blocks over 100,000 common advertising and tracking domains. You can expand coverage by adding curated adlists in Adlists under the Group Management menu:
- Smart TV and streaming device adlists — Filter out telemetry and ad beacons from smart television manufacturers and streaming dongles.
- Malicious domain and scam lists — Block newly registered phishing portals, malware distribution domains, and crypto-mining scripts.
- Mobile app tracking feeds — Prevent in-app diagnostic data collection and tracking SDKs embedded in mobile games and utilities.
- Whitelisting legitimate services — Occasionally, aggressive blocklists might interfere with email affiliate links or video streaming applications. Use the Domains tab in Pi-hole to whitelist specific domains (such as Microsoft Update or streaming service authentication endpoints) with regex or exact matches.
High Availability and Redundancy Setup
Because your entire home network relies on functional DNS resolution to load web pages and connect to cloud endpoints, deploying a high-availability secondary Pi-hole is a smart homelab upgrade.
Running a secondary instance on an alternate hardware device (such as a second mini PC or a spare development board) provides fault tolerance. Using community tools like gravity-sync allows both instances to continuously mirror custom blocklists, local DNS records, and whitelists across your network. In your router DHCP server configuration, list the primary Pi-hole as DNS 1 and the secondary Pi-hole as DNS 2. If the primary host undergoes maintenance or reboot cycles, network traffic seamlessly fails over to the secondary node without interruption.
Useful Documentation and Technical References
For deeper configuration and community blocklists, reference these verified resources:
- Pi-hole Official Documentation — Complete manual covering Pi-hole core features, FTL configuration, and command line tools.
- Pi-hole Docker Repository — Official container maintenance guidelines, environment variables, and release tags.
- Unbound DNS Resolver Documentation — Implementation guide for building a local validating recursive caching DNS resolver.
- Quad9 DNS Features and Privacy — Information regarding threat-blocking upstream anycast DNS infrastructure.
Frequently Asked Questions
Can Pi-hole block YouTube ads on smart TVs and mobile apps?
Pi-hole cannot completely block YouTube advertisements on streaming devices and mobile apps. YouTube delivers video ads from the exact same domains and content delivery servers as the actual video stream. Blocking the ad domain names at the DNS level results in breaking the video playback entirely. To block YouTube ads effectively, browser-based extension script blockers or dedicated alternative frontends are required.
What happens if the Pi-hole server goes down?
If your Pi-hole host server loses power or goes offline, devices configured to use it as their sole DNS server will not be able to resolve domain names, causing internet access to appear completely broken. To eliminate single points of failure, many homelab administrators deploy two redundant Pi-hole instances running on separate physical hardware (e.g., a primary mini PC and a secondary low-cost appliance) synced via gravity-sync.
Will Pi-hole slow down my internet browsing speed?
No. In fact, Pi-hole generally speeds up page load times across your home network. By blocking heavy third-party tracking scripts and ad multimedia files before they download, less bandwidth is consumed. Furthermore, Pi-hole caches frequently requested DNS records locally in RAM, responding to repeated queries in less than one millisecond.
Can I set up Pi-hole alongside a VPN?
Yes. Running WireGuard or Tailscale alongside Pi-hole allows you to route DNS queries from mobile devices back through your home Pi-hole instance even when connected to cellular networks or public Wi-Fi hotspots. This provides network-wide ad blocking on your smartphone wherever you travel.
How do I update Pi-hole blocklists?
Pi-hole automatically updates its gravity blocklist database once a week during early morning hours via an automated cron job. You can also manually trigger a blocklist update at any time by navigating to Tools → Update Gravity in the web dashboard or running pihole -g via the terminal.
2 Comments
Comments are closed.